CloudWatch-native alerts & log search
Native support for CloudWatch alerts and logs with no log extraction.
Security operations for AWS
uRisco SecurityOps helps teams search CloudWatch logs, detect suspicious activity, and automatically analyze alerts with AI — without log extraction, manual query writing, or complex learning curves.
No log extraction
 Visual log search
 No query language required
 Private deployment on AWS
Private deployment
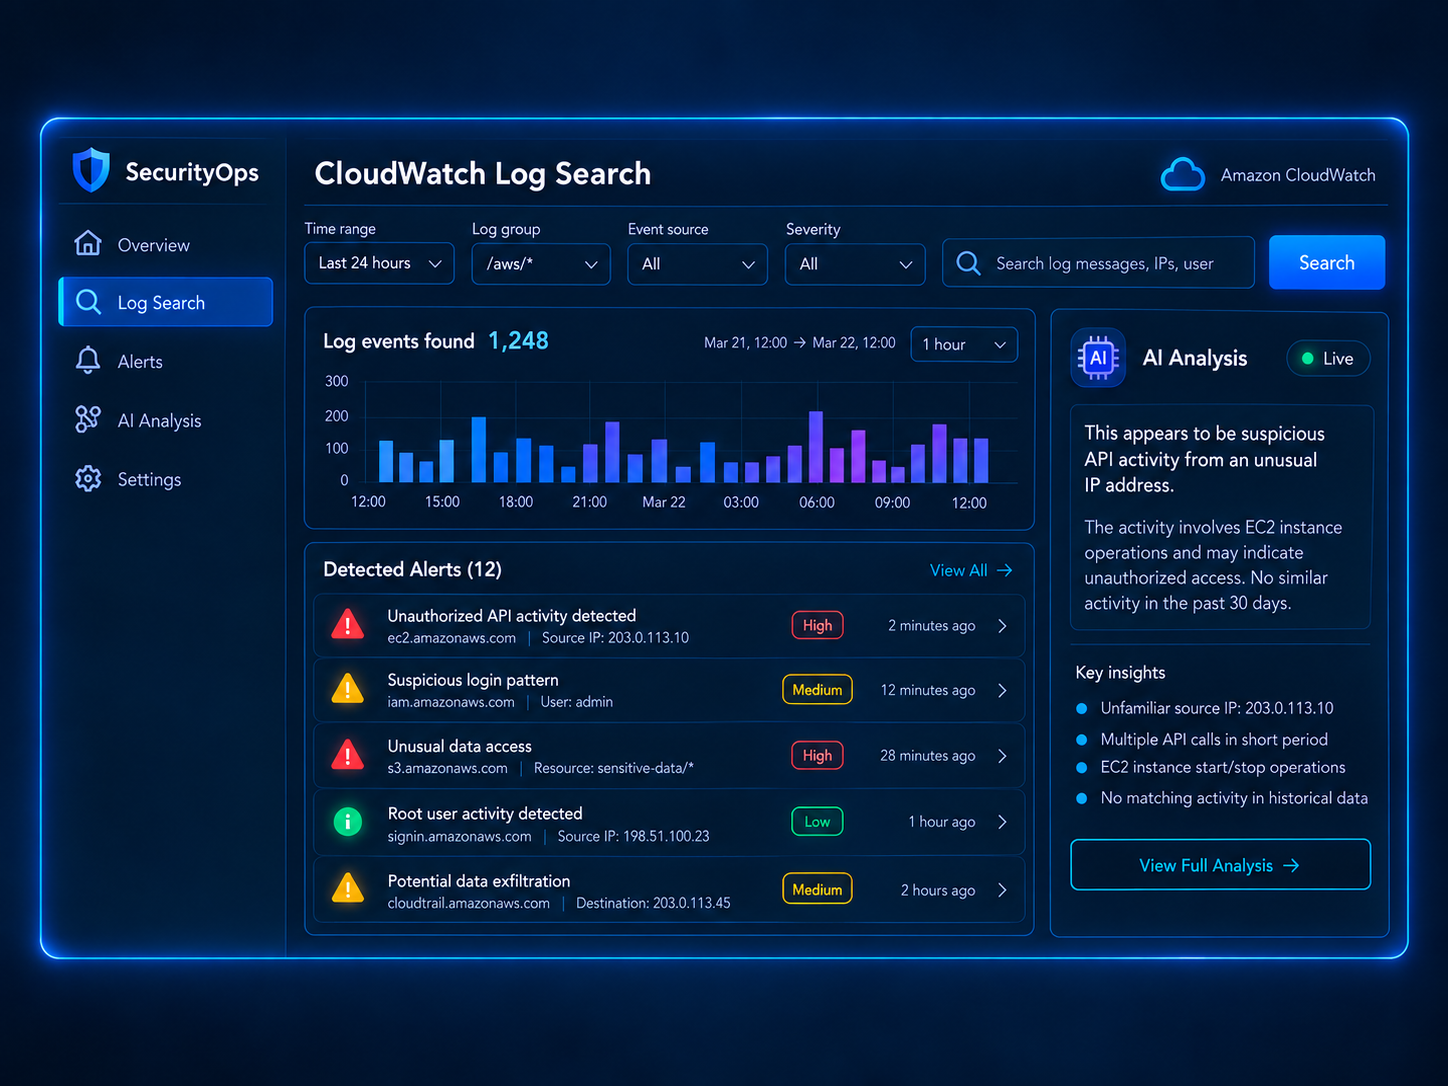
Native support for CloudWatch alerts and logs with no log extraction.
Automatically analyze alerts with AI and push the analysis result to your team.
Filter-based search and visual operation. No need to write query statements or learn a new language.
Subscribe via AWS Marketplace and deploy privately in your AWS environment.
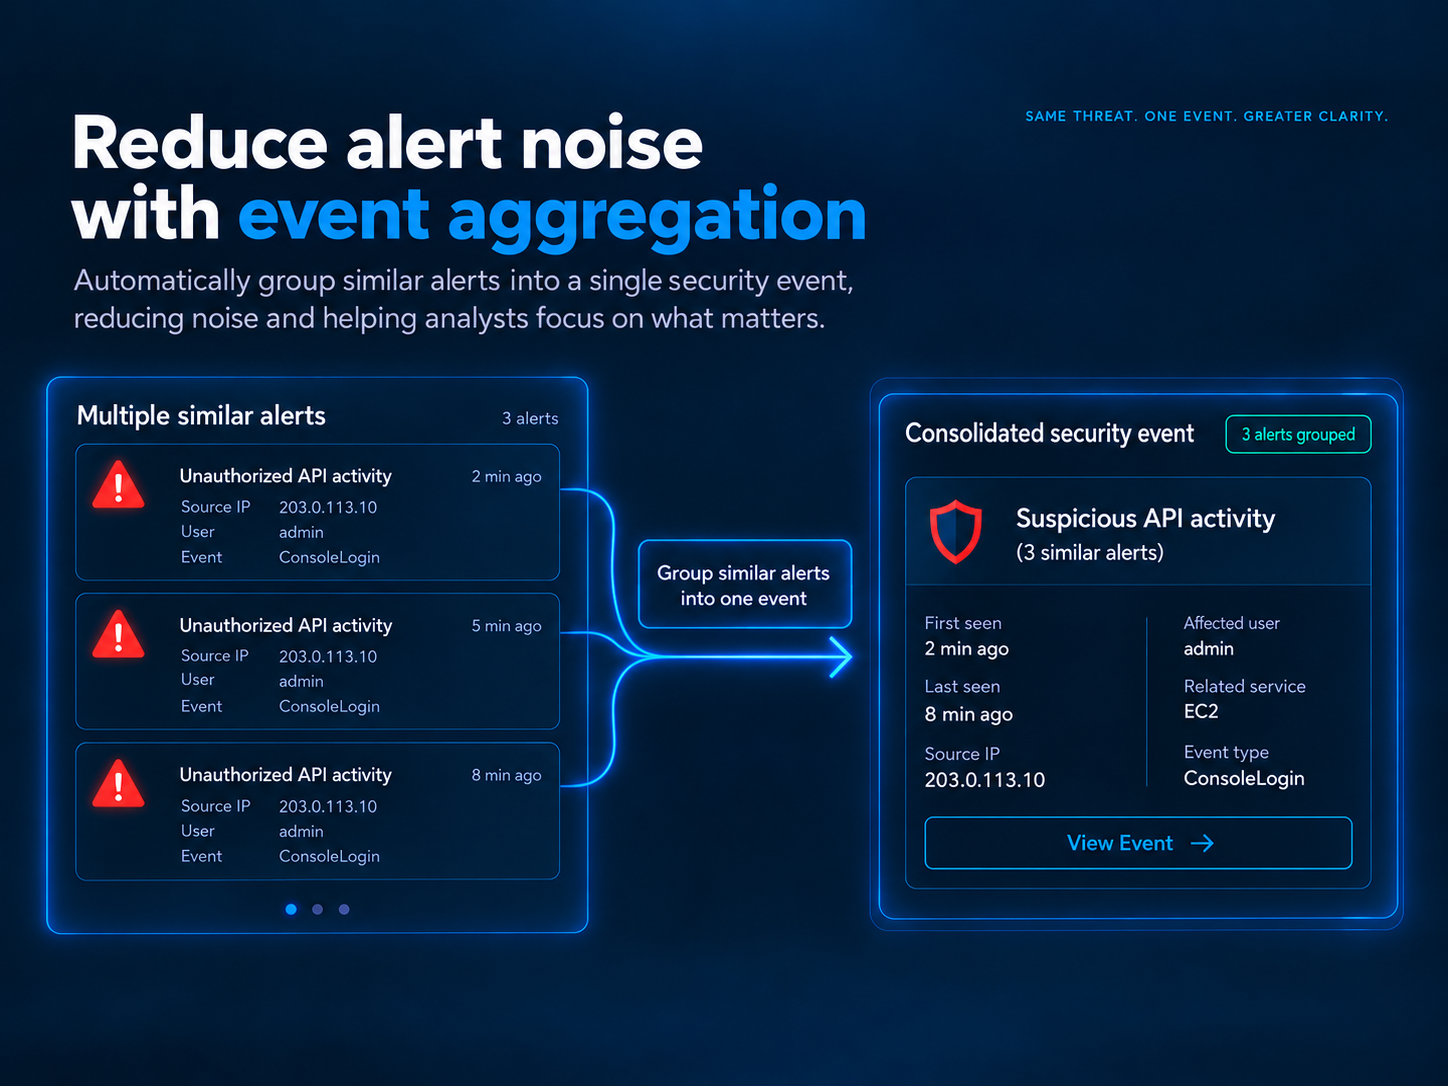
Automatically group similar alerts into a single security event, reducing noise and helping analysts focus on what matters.
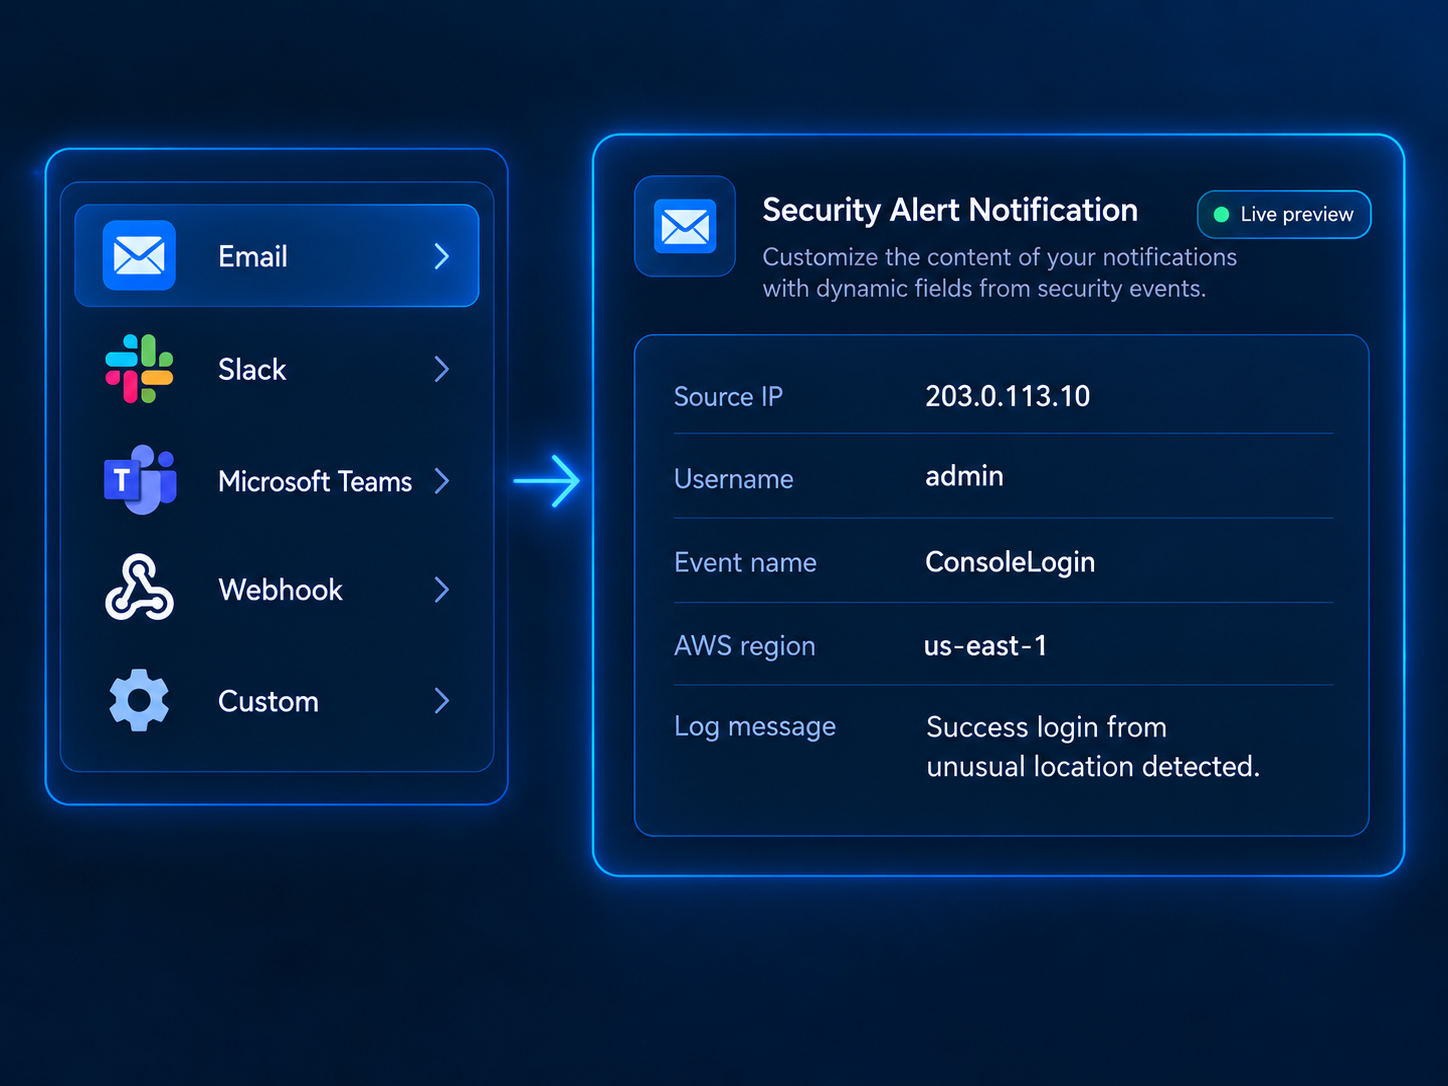
Choose from multiple alerting modes and configure notification rules. Customize alert content and select specific log fields — such as source IP, username, event name, region, or log message — to include in your notifications.
Detect vulnerabilities in containers and development projects.
Encryption and decryption utilities for secure operations.
Permission management and audit logging.
Product walkthroughs and deployment demos.
▶
Search AWS CloudWatch logs visually without extracting log data or writing query language.
www.youtube.com/watch?v=logsearch-demo ↗
▶
Use AI-assisted analysis to summarize alerts, explain evidence, and accelerate triage.
www.youtube.com/watch?v=ai-alert-demo ↗Deploy SecurityOps privately in your AWS environment with marketplace-friendly adoption.
www.youtube.com/watch?v=private-aws-demo ↗
▶
Move from suspicious event to log context with guided visual investigation flows.
www.youtube.com/watch?v=visual-investigation-demo ↗
▶
Customize alert notifications with the fields and context each response team needs.
www.youtube.com/watch?v=custom-notification-demo ↗Private, secure, and easy to adopt.
Secure AWS today. Stronger teams tomorrow.